ACLs & wildcard masks
Use this when: you permit or deny traffic on a router or switch, or lock down who can SSH to it.
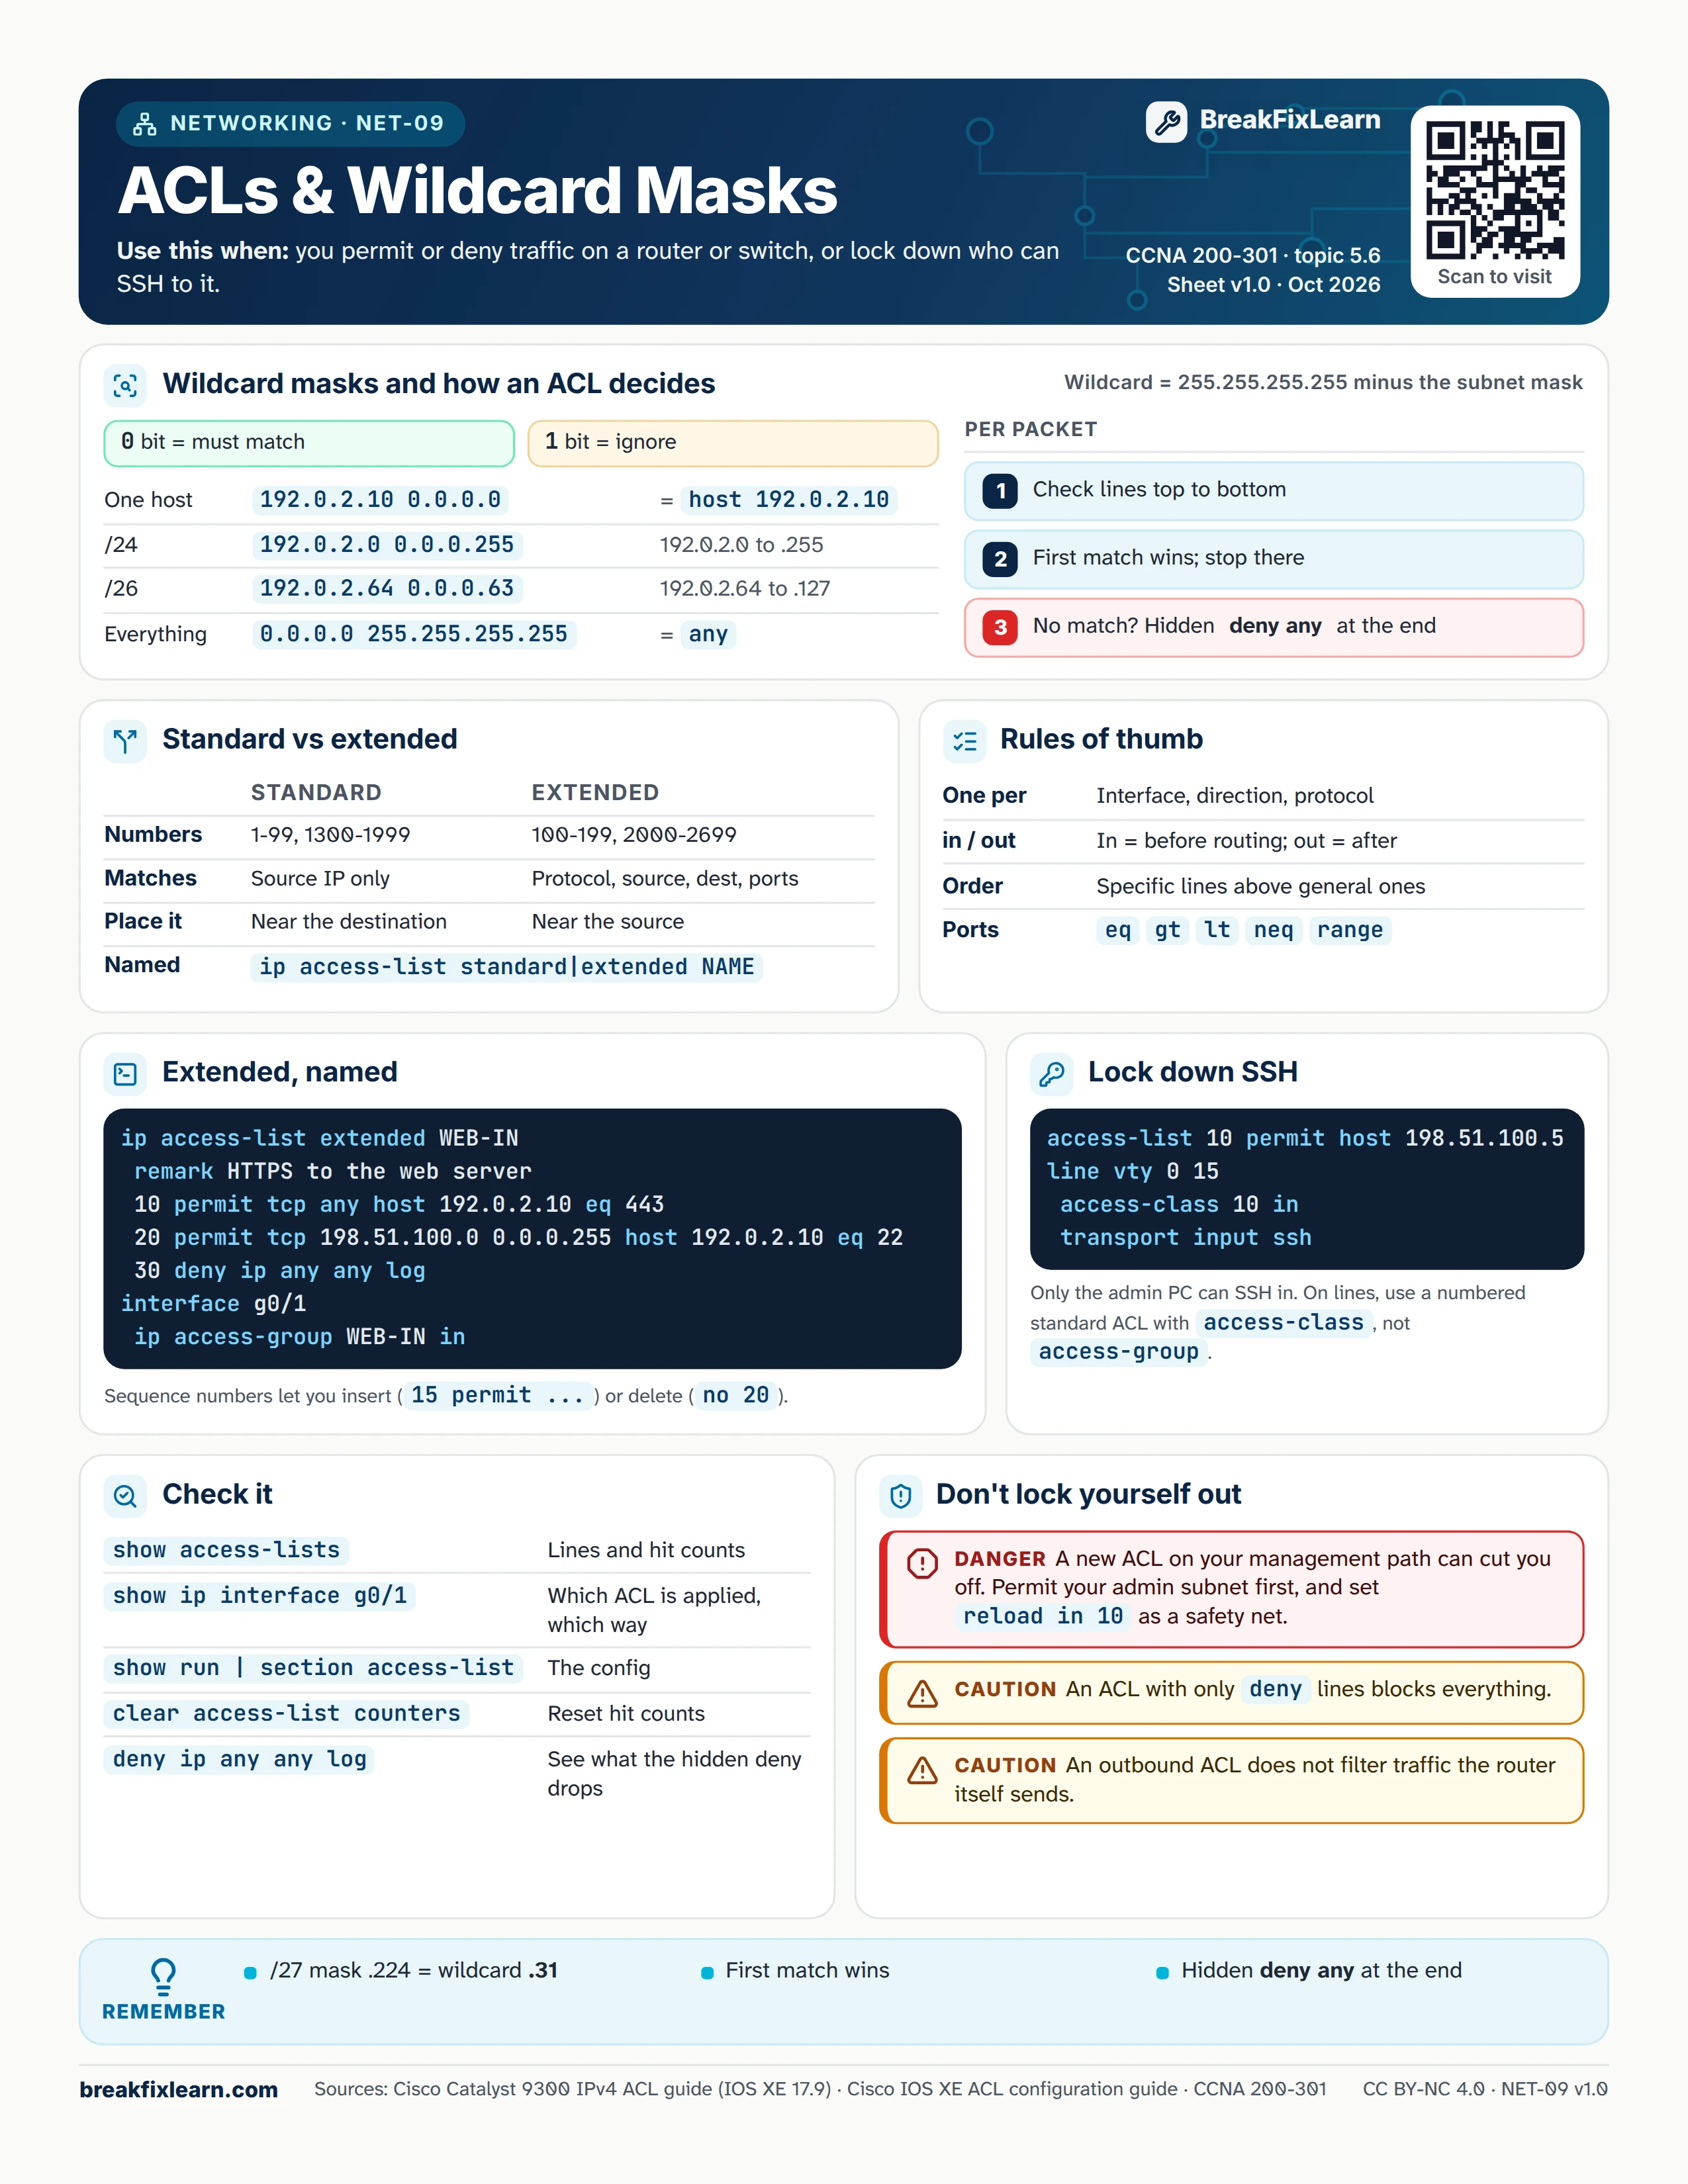
Text version
Everything on the sheet, as plain HTML: handy for screen readers, copy-paste and search.
Wildcard masks
A 0 bit means the address bit must match; a 1 bit means ignore it. Wildcard = 255.255.255.255 minus the subnet mask.
| Match | Address and wildcard | Covers |
|---|---|---|
| One host | 192.0.2.10 0.0.0.0 | Same as host 192.0.2.10 |
| /24 | 192.0.2.0 0.0.0.255 | 192.0.2.0 to .255 |
| /26 | 192.0.2.64 0.0.0.63 | 192.0.2.64 to .127 |
| Everything | 0.0.0.0 255.255.255.255 | Same as any |
How an ACL decides
- It checks lines from top to bottom.
- The first match wins, and checking stops there.
- No match? A hidden
deny anyat the end drops the packet.
Standard vs extended
| Standard | Extended | |
|---|---|---|
| Numbers | 1-99, 1300-1999 | 100-199, 2000-2699 |
| Matches | Source IP only | Protocol, source, destination, ports |
| Place it | Near the destination | Near the source |
Named ACLs: ip access-list standard NAME or ip access-list extended NAME.
Rules of thumb
- One ACL per interface, per direction, per protocol
- Inbound ACLs run before routing; outbound after
- Put specific lines above general ones
- Port operators:
eq,gt,lt,neq,range
Extended, named ACL
ip access-list extended WEB-INremark HTTPS to the web server10 permit tcp any host 192.0.2.10 eq 44320 permit tcp 198.51.100.0 0.0.0.255 host 192.0.2.10 eq 2230 deny ip any any loginterface g0/1, thenip access-group WEB-IN in
Sequence numbers let you insert a line (15 permit ...) or delete one (no 20).
Lock down SSH
access-list 10 permit host 198.51.100.5line vty 0 15, thenaccess-class 10 inandtransport input ssh
Only the admin PC can SSH in. On lines, use a numbered standard ACL with access-class, not access-group.
Check it
| Command | Shows |
|---|---|
show access-lists | Lines and hit counts |
show ip interface g0/1 | Which ACL is applied, and which way |
show run | section access-list | The config |
clear access-list counters | Reset hit counts |
deny ip any any log | See what the hidden deny drops |
Don't lock yourself out
Danger. A new ACL on your management path can cut you off. Permit your admin subnet first, and set reload in 10 as a safety net.
Caution. An ACL with only deny lines blocks everything.
Caution. An outbound ACL does not filter traffic the router itself sends.
Remember
- /27 mask .224 = wildcard .31
- First match wins
- Hidden deny any at the end