Common attacks & mitigations (MITRE ATT&CK)
Use this when: you map an alert or incident to MITRE ATT&CK, or need the controls that stop the attacks seen most.
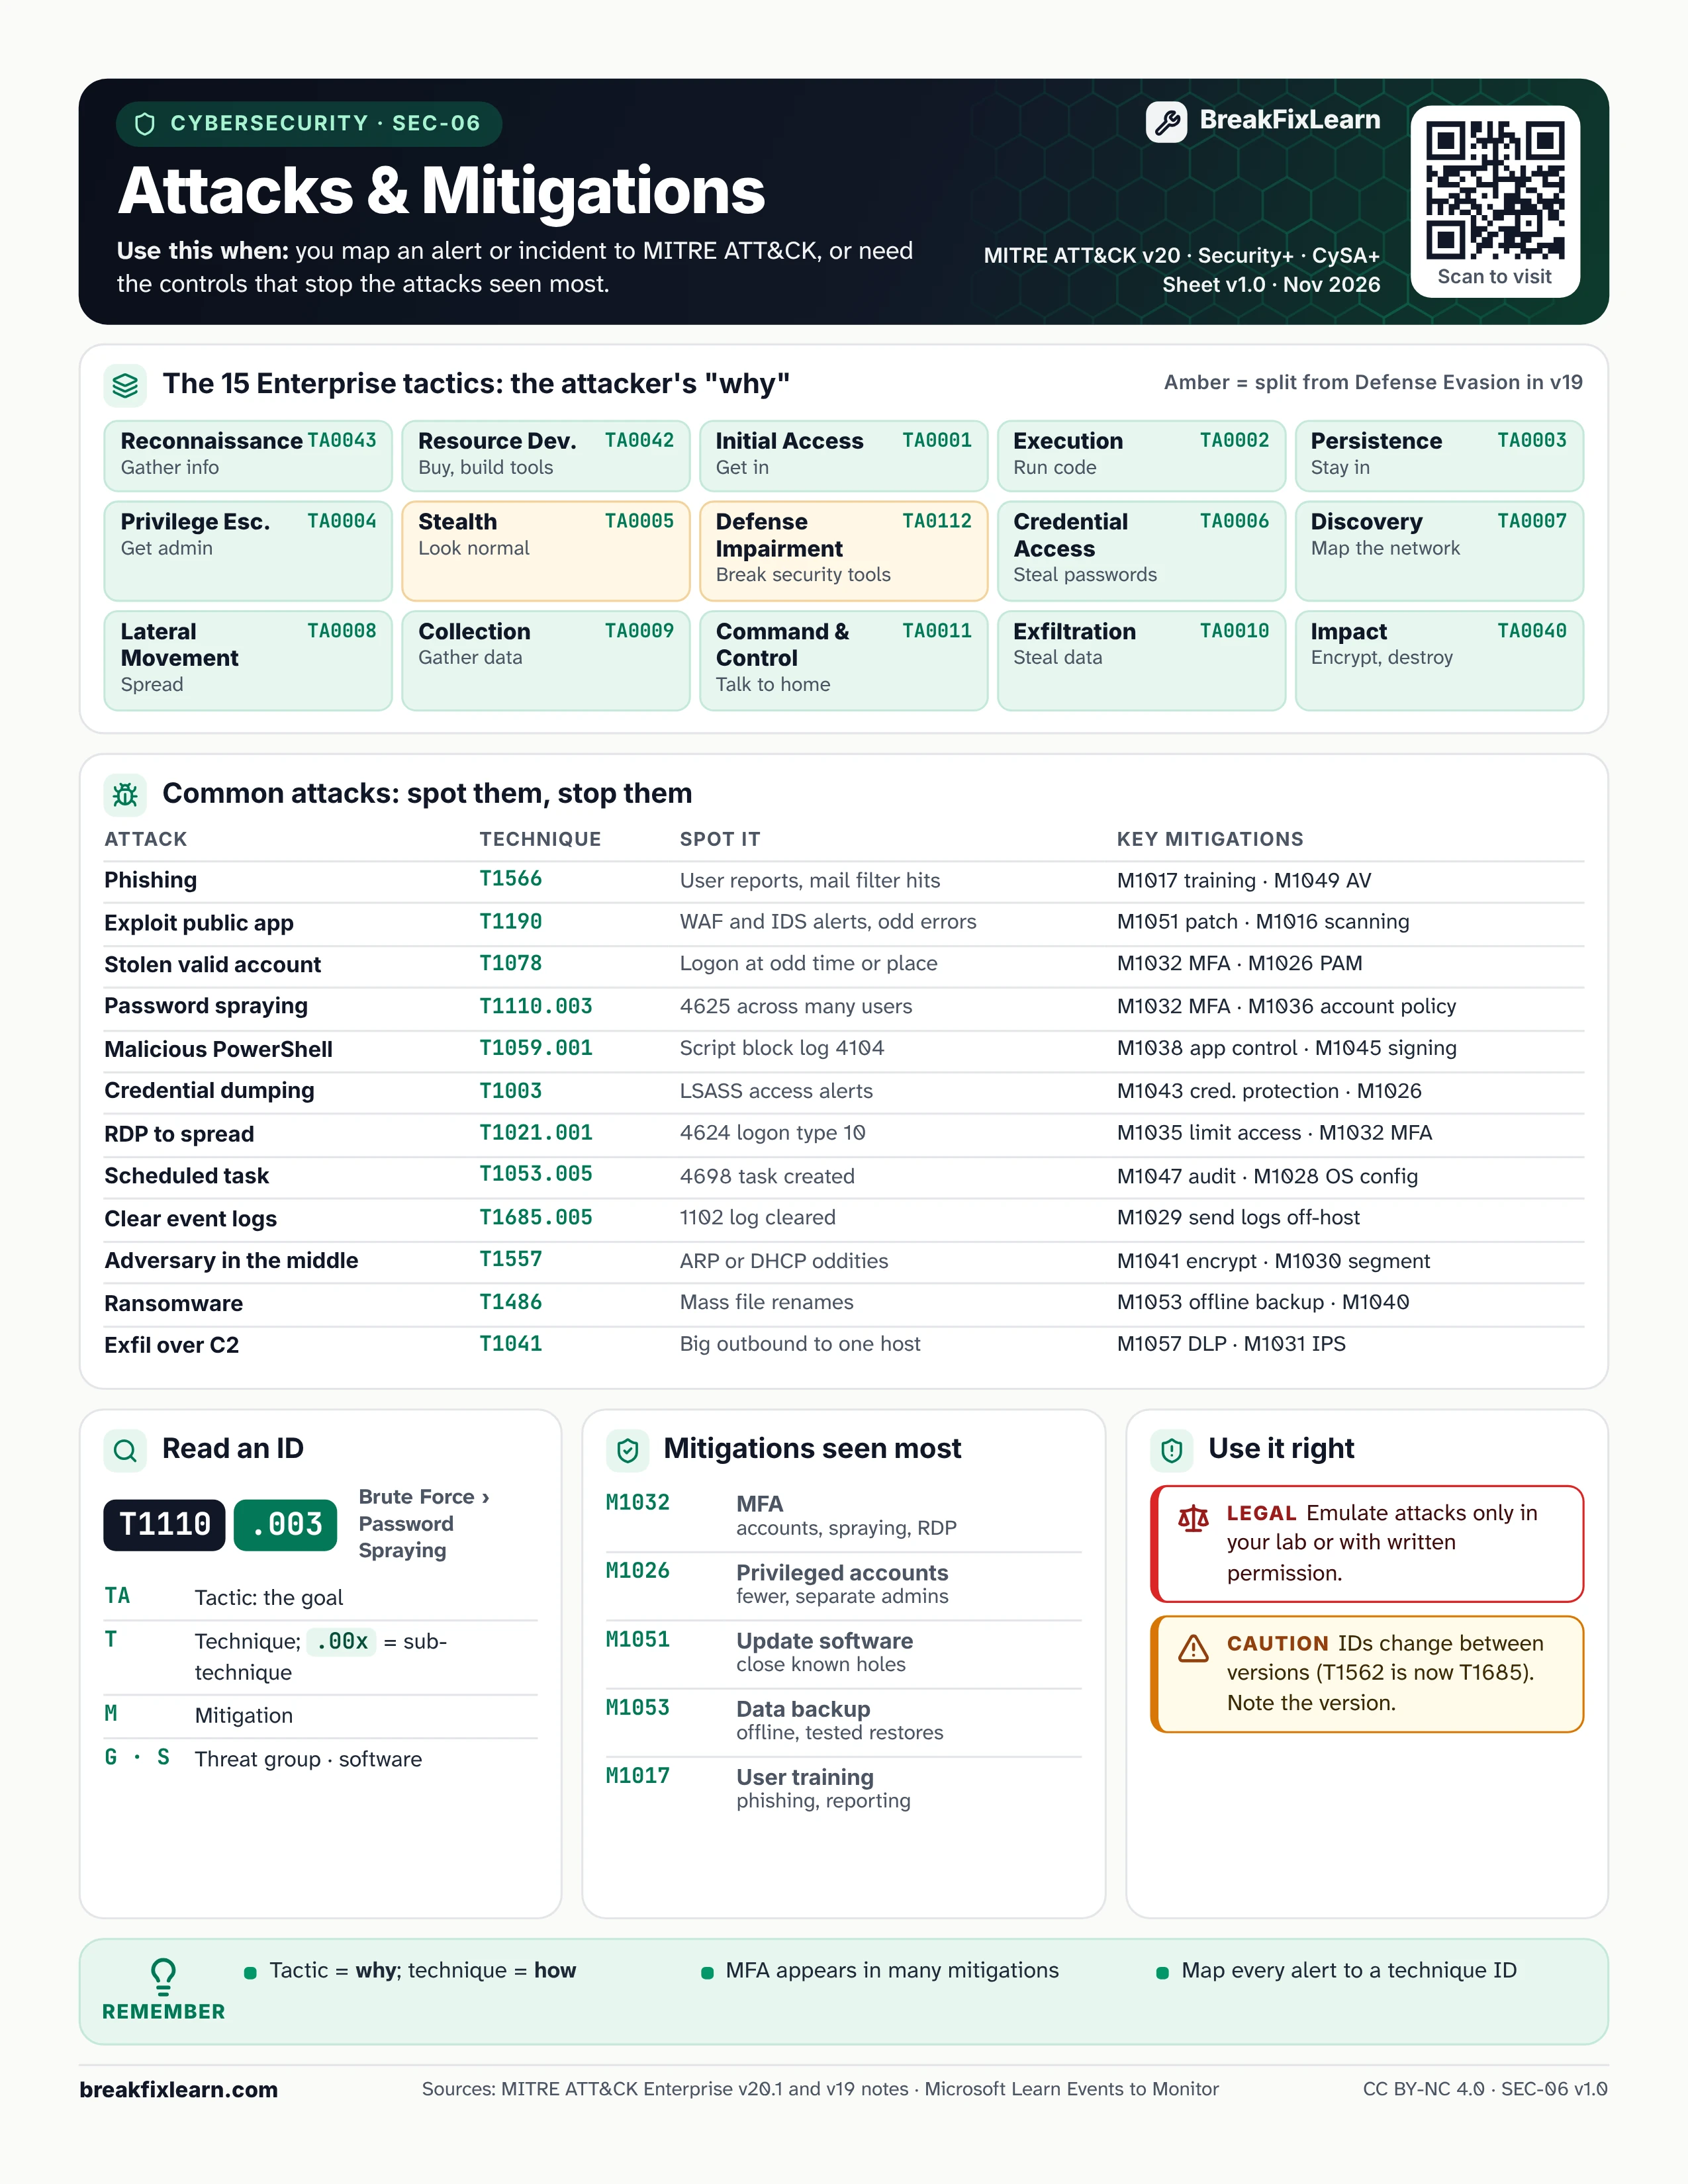
Text version
Everything on the sheet, as plain HTML: handy for screen readers, copy-paste and search.
The 15 Enterprise tactics
Tactics are the attacker's goal (the "why"). ATT&CK v19 (April 2026) split Defense Evasion into Stealth and Defense Impairment. Checked against ATT&CK v20.1.
| ID | Tactic | Goal |
|---|---|---|
| TA0043 | Reconnaissance | Gather information |
| TA0042 | Resource Development | Buy or build tools |
| TA0001 | Initial Access | Get in |
| TA0002 | Execution | Run code |
| TA0003 | Persistence | Stay in |
| TA0004 | Privilege Escalation | Get admin |
| TA0005 | Stealth | Look normal |
| TA0112 | Defense Impairment | Break security tools |
| TA0006 | Credential Access | Steal passwords |
| TA0007 | Discovery | Map the network |
| TA0008 | Lateral Movement | Spread |
| TA0009 | Collection | Gather data |
| TA0011 | Command and Control | Talk to home |
| TA0010 | Exfiltration | Steal data |
| TA0040 | Impact | Encrypt, destroy |
Common attacks: spot them, stop them
| Attack | Technique | Spot it | Key mitigations |
|---|---|---|---|
| Phishing | T1566 | User reports, mail filter hits | M1017 user training, M1049 antivirus |
| Exploit a public app | T1190 | WAF and IDS alerts, odd errors | M1051 update software, M1016 vulnerability scanning |
| Stolen valid account | T1078 | Logon at an odd time or place | M1032 MFA, M1026 privileged account management |
| Password spraying | T1110.003 | 4625 across many users | M1032 MFA, M1036 account use policies |
| Malicious PowerShell | T1059.001 | Script block log 4104 | M1038 execution prevention, M1045 code signing |
| Credential dumping | T1003 | LSASS access alerts | M1043 credential access protection, M1026 |
| RDP to spread | T1021.001 | 4624 logon type 10 | M1035 limit access over the network, M1032 MFA |
| Scheduled task | T1053.005 | 4698 task created | M1047 audit, M1028 OS configuration |
| Clear event logs | T1685.005 | 1102 log cleared | M1029 remote data storage (send logs off-host) |
| Adversary in the middle | T1557 | ARP or DHCP oddities | M1041 encrypt, M1030 network segmentation |
| Ransomware | T1486 | Mass file renames | M1053 offline backup, M1040 behavior prevention |
| Exfiltration over C2 | T1041 | Big outbound transfer to one host | M1057 data loss prevention, M1031 intrusion prevention |
Read an ID
T1110.003 is technique T1110 (Brute Force), sub-technique .003 (Password Spraying).
- TA: tactic, the goal
- T: technique;
.00xis a sub-technique - M: mitigation
- G and S: threat group and software
Mitigations seen most
| ID | Mitigation | Helps against |
|---|---|---|
| M1032 | Multi-factor authentication | Stolen accounts, spraying, RDP |
| M1026 | Privileged account management | Fewer, separate admin accounts |
| M1051 | Update software | Known vulnerabilities |
| M1053 | Data backup | Ransomware; keep backups offline and test restores |
| M1017 | User training | Phishing; teach people to report |
Use it right
Authorized use only. Emulate attacks only in your lab or with written permission.
Caution. IDs change between versions (T1562 is now T1685). Note the ATT&CK version you used.
Remember
- Tactic = why; technique = how
- MFA appears in many mitigations
- Map every alert to a technique ID
Sources
- MITRE ATT&CK Enterprise tactics
- MITRE ATT&CK updates, April 2026 (v19)
- Microsoft Learn, Appendix L: Events to Monitor