OWASP Top 10 web risks
Use this when: you build, review or test a web app and need the ten most important risk areas, what they look like and how to fix them.
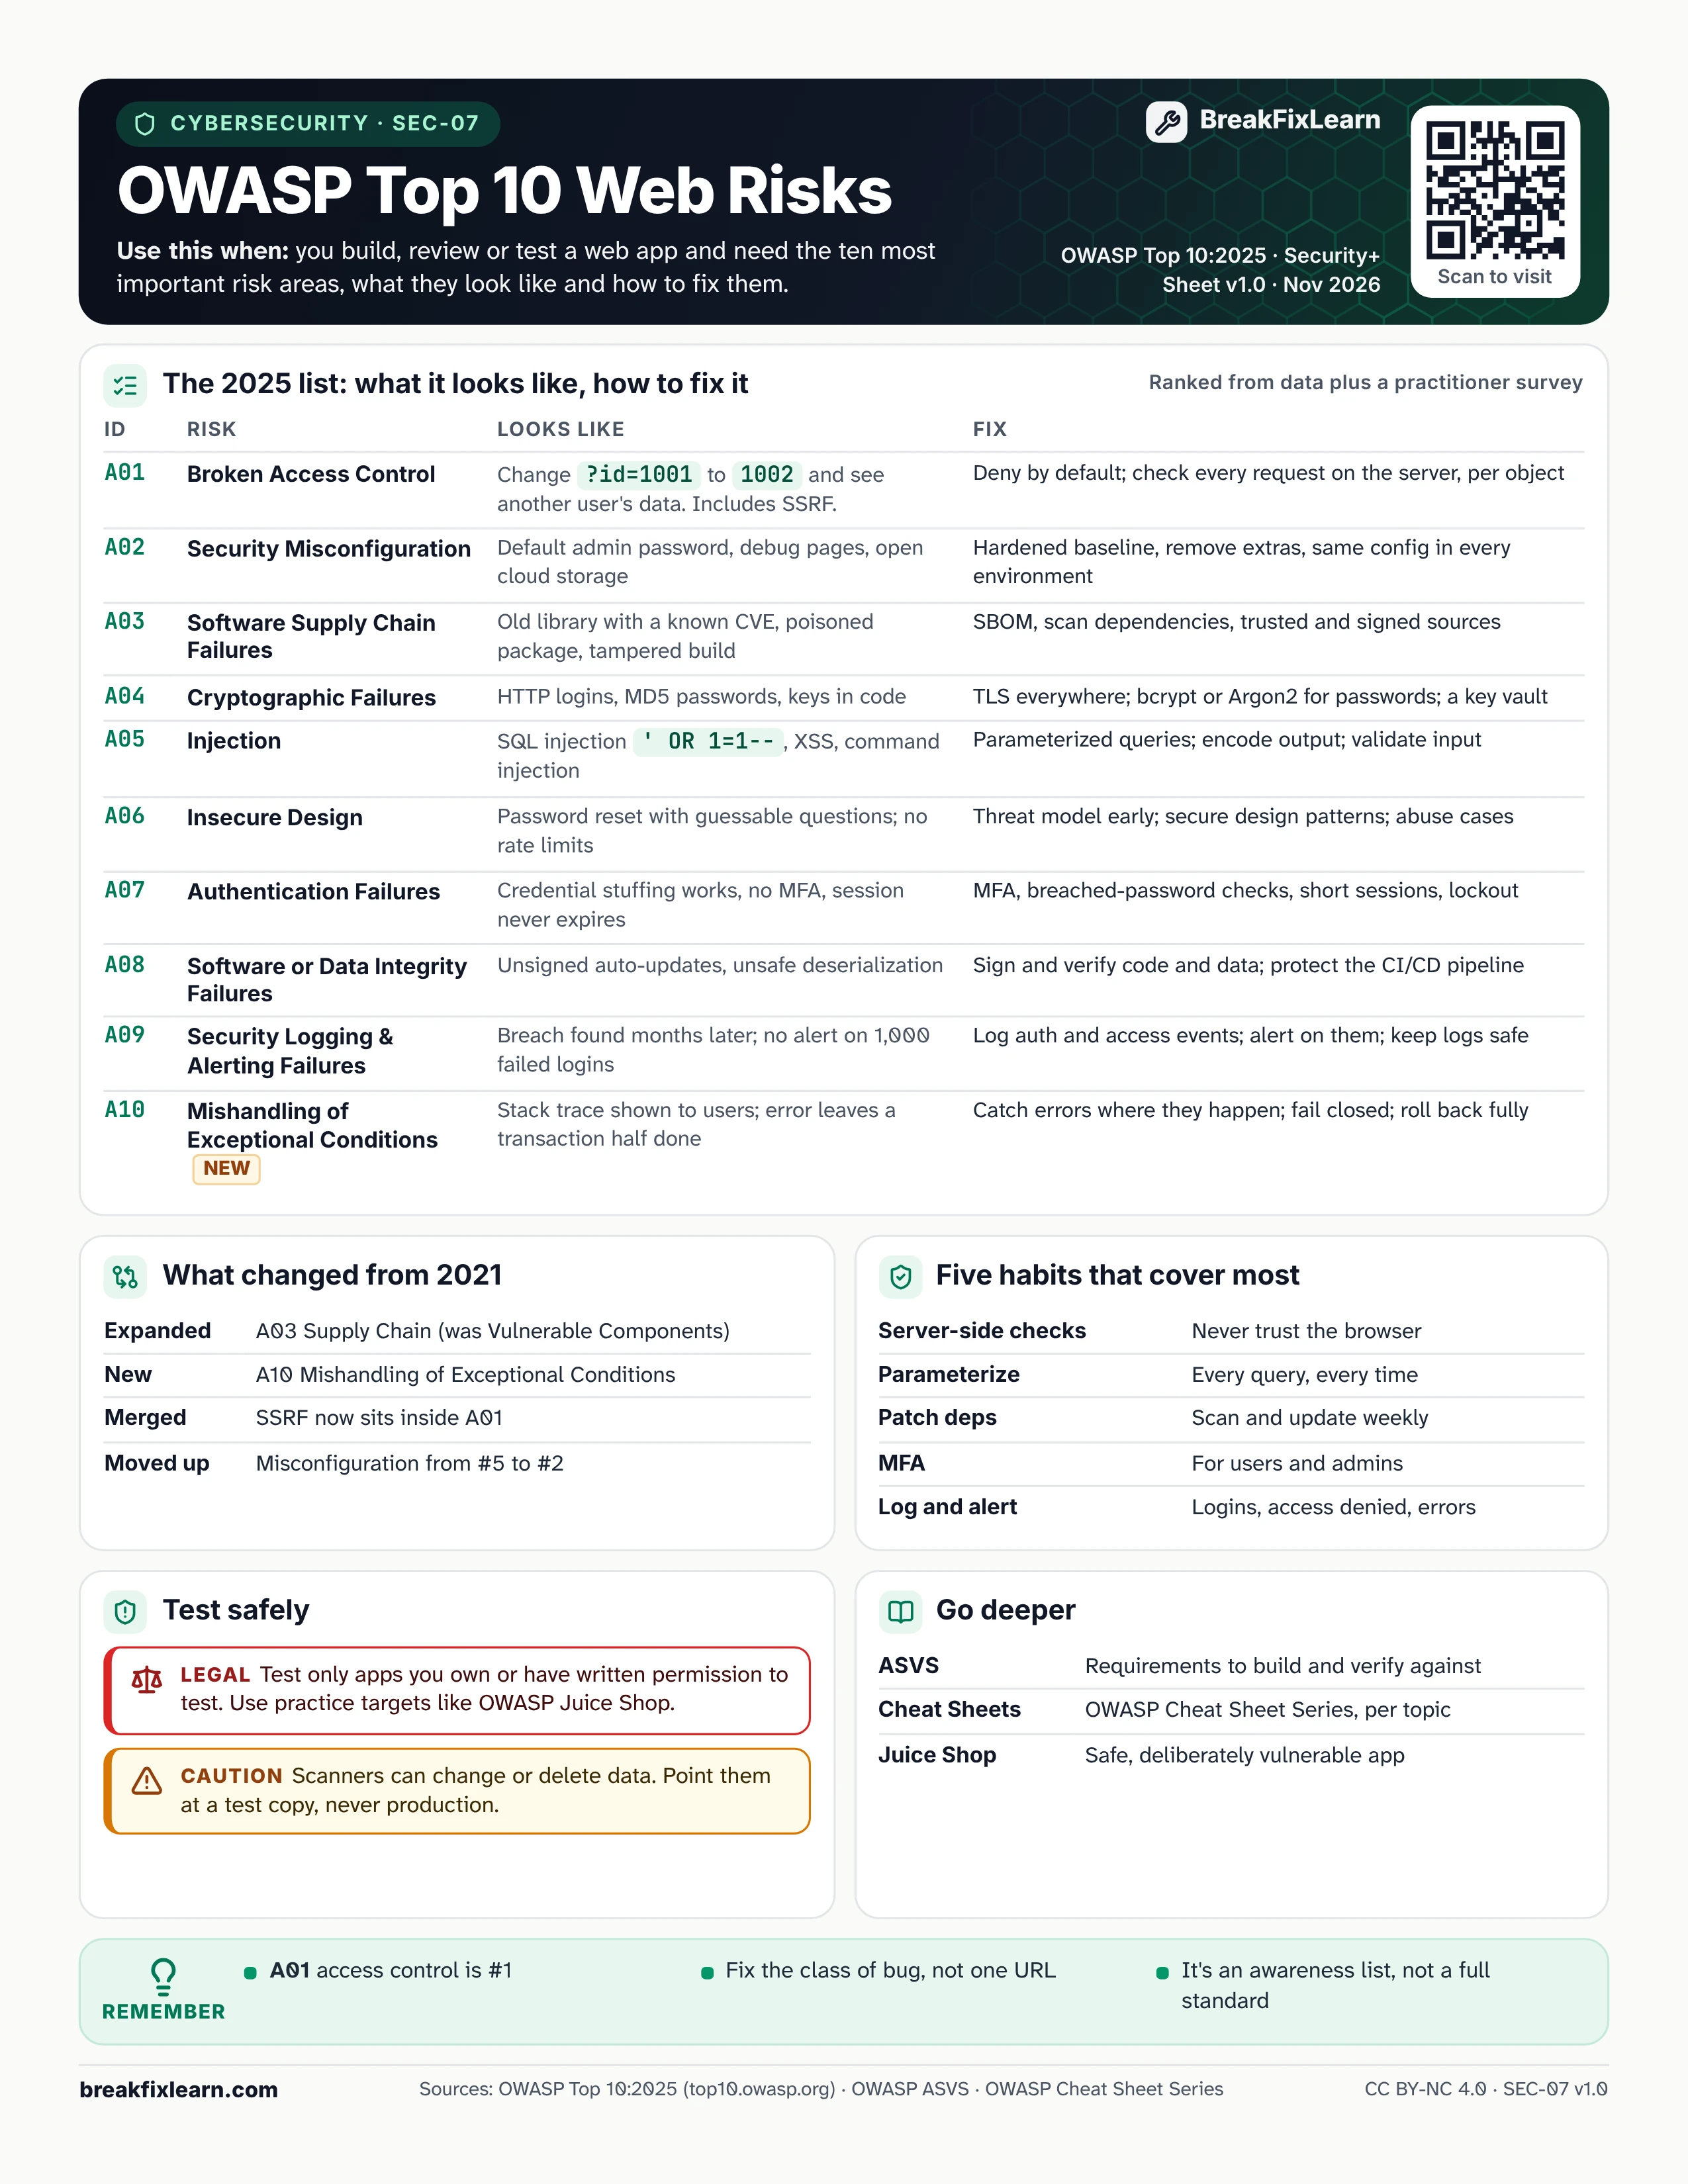
Text version
Everything on the sheet, as plain HTML: handy for screen readers, copy-paste and search.
The OWASP Top 10:2025
OWASP ranks the list from data plus a practitioner survey.
| ID | Risk | Looks like | Fix |
|---|---|---|---|
| A01 | Broken Access Control | Change ?id=1001 to 1002 and see another user's data. Includes SSRF. | Deny by default; check every request on the server, per object |
| A02 | Security Misconfiguration | Default admin password, debug pages, open cloud storage | Hardened baseline, remove extras, same config in every environment |
| A03 | Software Supply Chain Failures | Old library with a known CVE, poisoned package, tampered build | SBOM, scan dependencies, trusted and signed sources |
| A04 | Cryptographic Failures | HTTP logins, MD5 passwords, keys in code | TLS everywhere; bcrypt or Argon2 for passwords; a key vault |
| A05 | Injection | SQL injection (' OR 1=1--), XSS, command injection | Parameterized queries; encode output; validate input |
| A06 | Insecure Design | Password reset with guessable questions; no rate limits | Threat model early; secure design patterns; abuse cases |
| A07 | Authentication Failures | Credential stuffing works, no MFA, sessions never expire | MFA, breached-password checks, short sessions, lockout |
| A08 | Software or Data Integrity Failures | Unsigned auto-updates, unsafe deserialization | Sign and verify code and data; protect the CI/CD pipeline |
| A09 | Security Logging and Alerting Failures | Breach found months later; no alert on 1,000 failed logins | Log auth and access events; alert on them; keep logs safe |
| A10 | Mishandling of Exceptional Conditions (new) | Stack trace shown to users; an error leaves a transaction half done | Catch errors where they happen; fail closed; roll back fully |
What changed from 2021
- Expanded: A03 Software Supply Chain Failures grew from 2021's Vulnerable and Outdated Components.
- New: A10 Mishandling of Exceptional Conditions.
- Merged: SSRF now sits inside A01.
- Moved up: Security Misconfiguration went from #5 to #2.
Five habits that cover most
- Server-side checks: never trust the browser
- Parameterize: every query, every time
- Patch dependencies: scan and update weekly
- MFA: for users and admins
- Log and alert: logins, access denied, errors
Test safely
Authorized use only. Test only apps you own or have written permission to test. Use practice targets like OWASP Juice Shop.
Caution. Scanners can change or delete data. Point them at a test copy, never production.
Go deeper
- OWASP ASVS: requirements to build and verify against
- OWASP Cheat Sheet Series: guidance per topic
- OWASP Juice Shop: a safe, deliberately vulnerable app
Remember
- A01 Broken Access Control is #1
- Fix the class of bug, not one URL
- The Top 10 is an awareness list, not a full standard